

Updated JN0-637 Dumps PDF - JN0-637 Real Valid Brain Dumps With 125 Questions!
100% Free JN0-637 Exam Dumps Use Real JNCIP-SEC Dumps
NEW QUESTION # 37
Click the Exhibit button.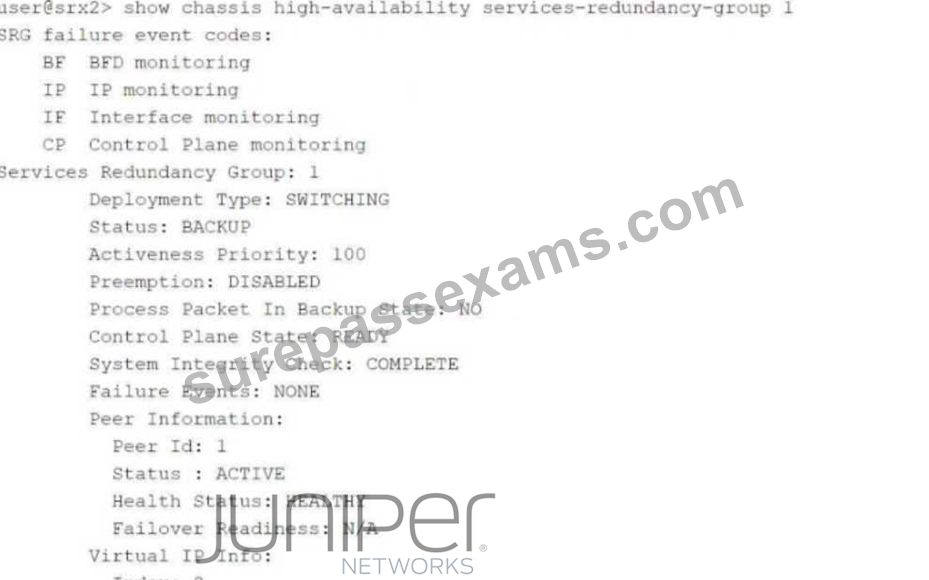
Referring to the exhibit, which two statements are correct? (Choose two.)
- A. The ge-0/0/3.0 and ge-0/0/4.0 interfaces are active and will respond to ARP requests to the virtual IP MAC address.
- B. This device is the active node for SRG1.
- C. This device is the backup node for SRG1.
- D. The ge-0/0/3.0 and ge-0/0/4.0 interfaces are not active and will not respond to ARP requests to the virtual IP MAC address.
Answer: A,B
NEW QUESTION # 38
Exhibit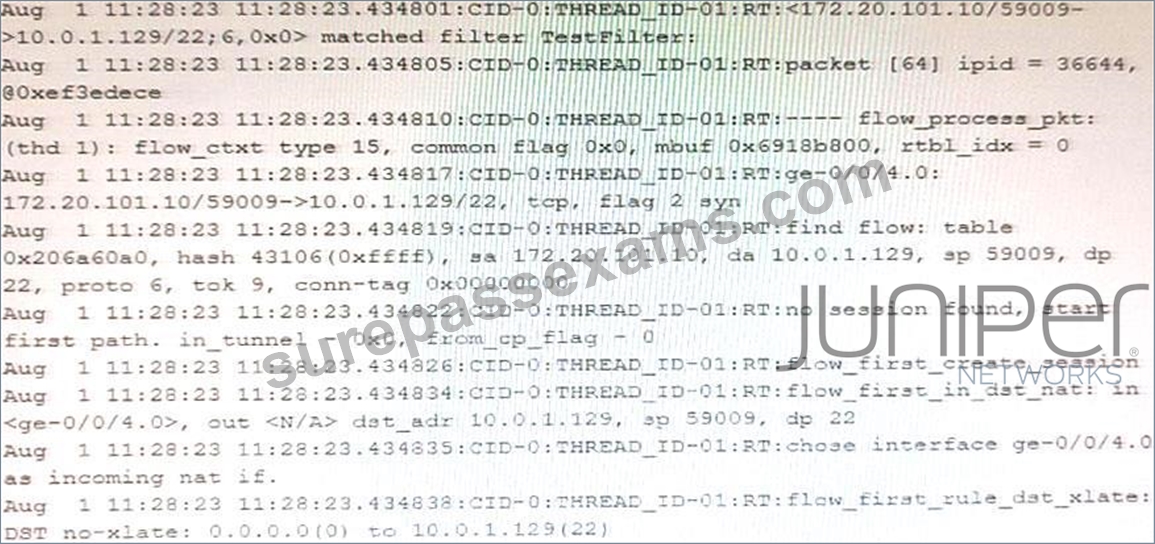
The exhibit shows a snippet of a security flow trace.
In this scenario, which two statements are correct? (Choose two.)
- A. An existing session is found in the table.
- B. This packet arrived on interface ge-0/0/4.0.
- C. Destination NAT occurs.
- D. The capture is a packet from the source address 172.20.101.10 destined to 10.0.1.129.
Answer: A,D
NEW QUESTION # 39
Exhibit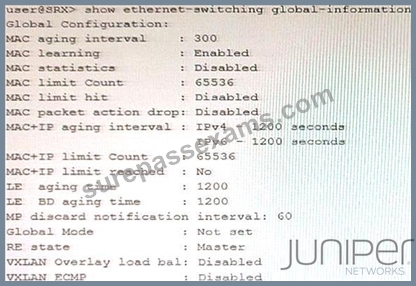
You have configured the SRX Series device to switch packets for multiple directly connected hosts that are within the same broadcast domain However, the traffic between two hosts in the same broadcast domain are not matching any security policies Referring to the exhibit, what should you do to solve this problem?
- A. You must change the global mode to switching mode.
- B. You must change the global mode to security switching mode.
- C. You must change the global mode to transparent bridge mode.
- D. You must change the global mode to security bridging mode
Answer: D
NEW QUESTION # 40
Exhibit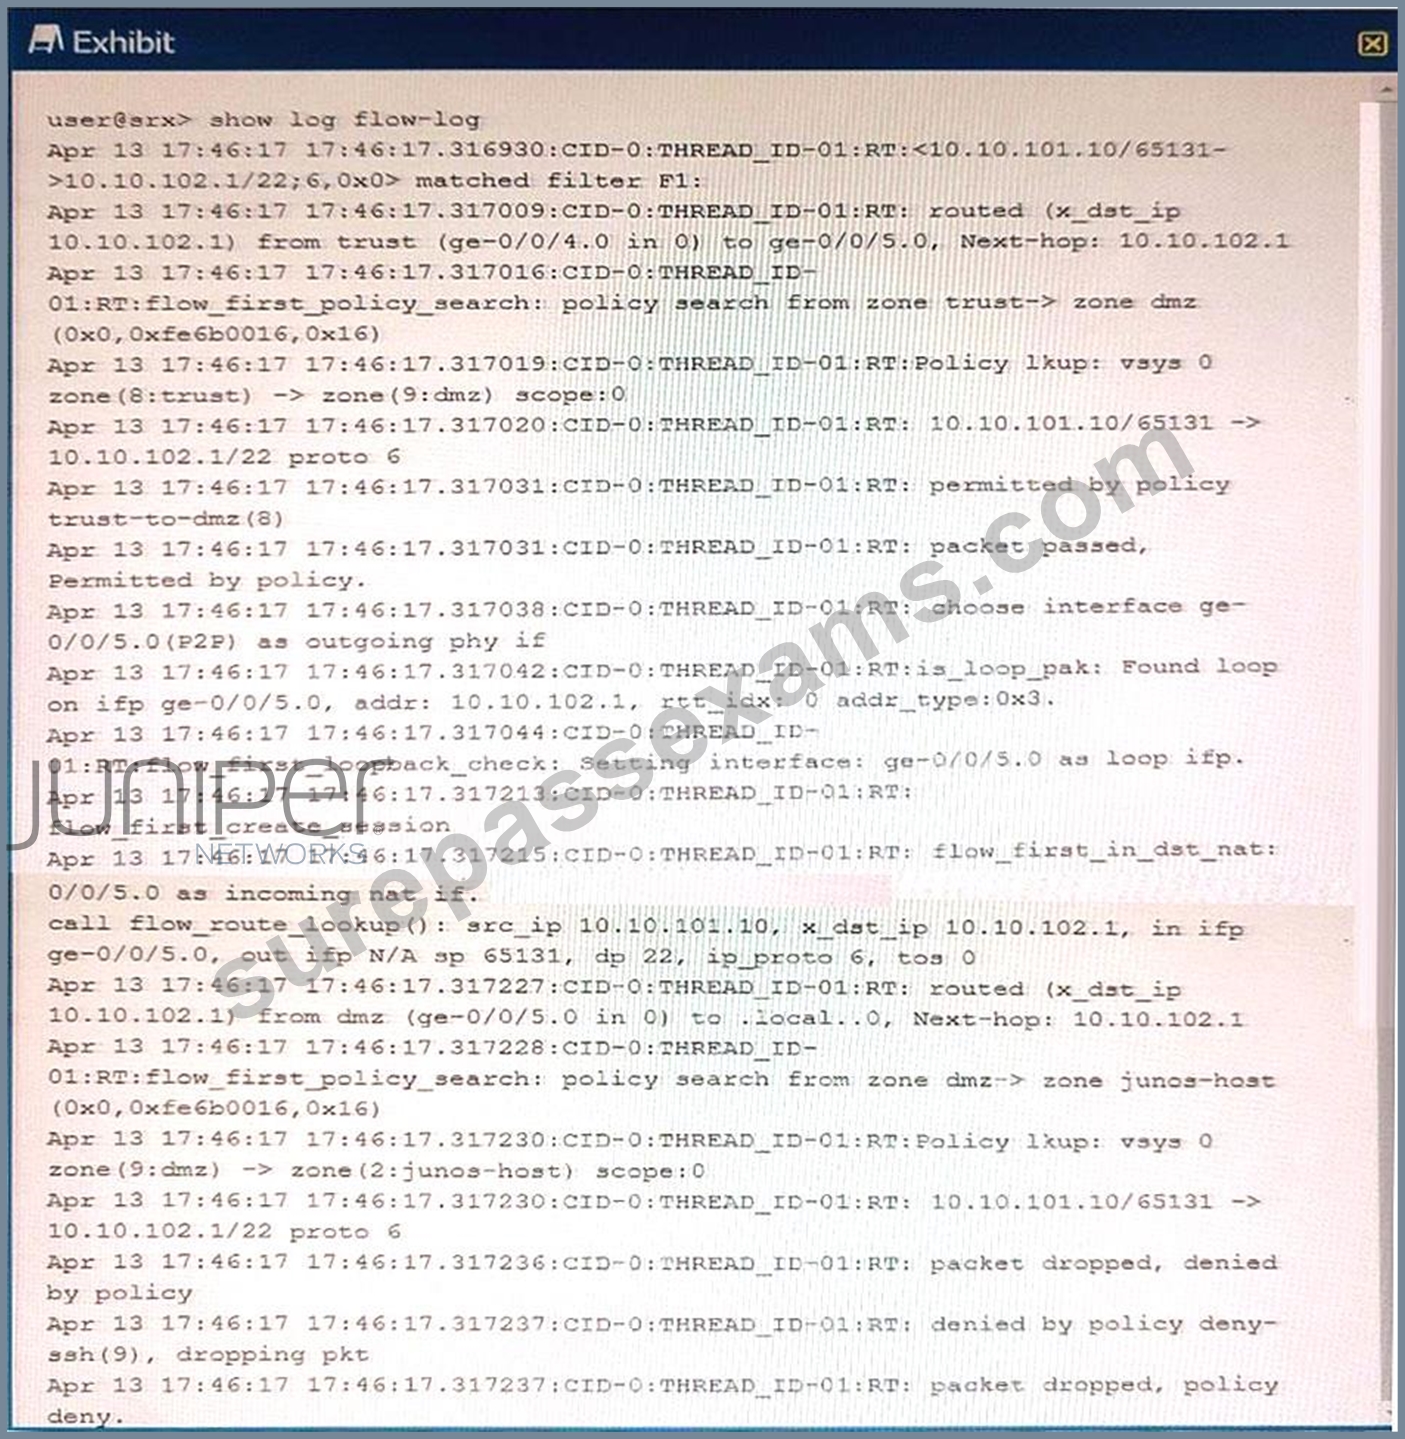
Referring to the exhibit, which three statements are true? (Choose three.)
- A. The packet's destination is to a server in the DMZ zone.
- B. The packet is allowed to make an SSH connection.
- C. The packet is dropped before making an SSH connection.
- D. The packet originated within the Trust zone.
- E. The packet's destination is to an interface on the SRX Series device.
Answer: C,D,E
NEW QUESTION # 41
You configured a chassis cluster for high availability on an SRX Series device and enrolled this HA cluster with the Juniper ATP Cloud.
Which two statements are correct in this scenario? (Choose two.)
- A. You must use the same license key on both cluster nodes.
- B. You must use different license keys on both cluster nodes.
- C. You must set up your HA cluster after enrolling your devices with Juniper ATP Cloud
- D. When enrolling your devices, you only need to enroll one node.
Answer: A,D
NEW QUESTION # 42
Referring to the exhibit, you have been assigned the user LogicalSYS1 credentials shown in the configuration.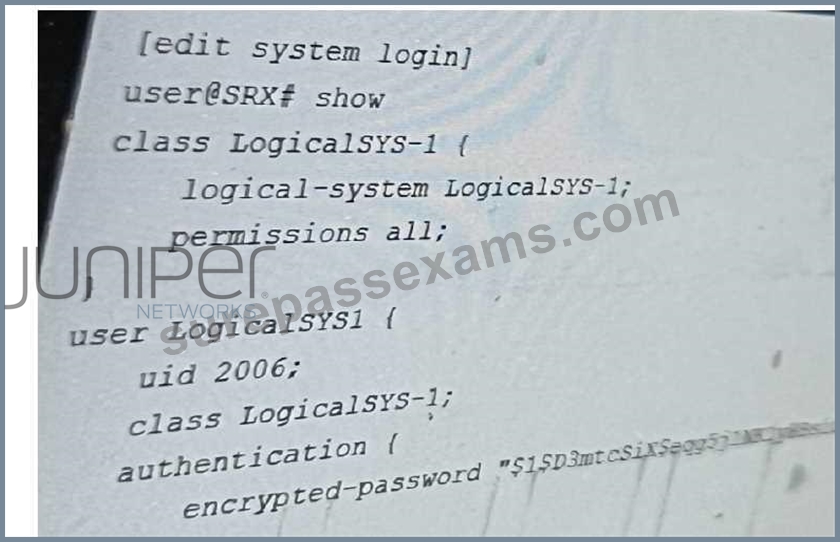
In this scenario, which two statements are correct? (Choose two.)
- A. When you log in to the device, you will be located at the operational mode of the Logic
- B. When you log in to the device, you will be permitted to view only the routing tables for Logic
- C. When you log in to the device, you will be located at the operational mode of the main system
- D. When you log in to the device, you will be permitted to view all routing tables available on the SRX device
Answer: A,B
NEW QUESTION # 43
Which Junos security feature is used for signature-based attack prevention?
- A. IPS
- B. PIM
- C. RADIUS
- D. AppQoS
Answer: A
NEW QUESTION # 44
Exhibit: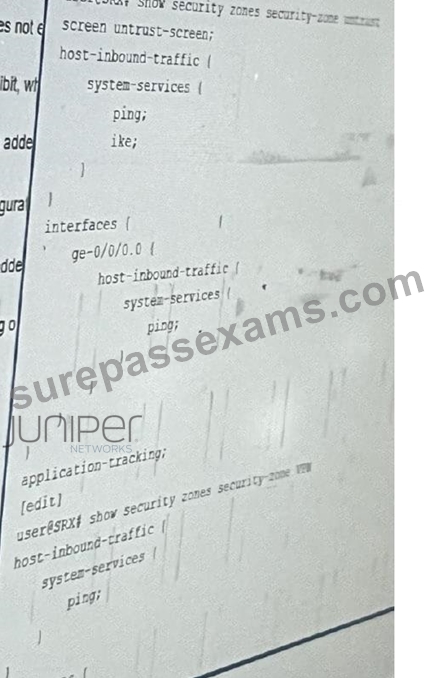
The Ipsec VPN does not establish when the peer initiates, but it does establish when the SRX series device initiates. Referring to the exhibit, what will solve this problem?
- A. IKE needs to be added for the host-inbound traffic on the VPN zone.
- B. Application tracking on the untrust zone needs to be removed.
- C. The screen configuration on the untrust zone needs to be modified.
- D. IKE needs to be added to the host-inbound traffic directly on the ge-0/0/0 interface.
Answer: D
NEW QUESTION # 45
You are asked to connect two hosts that are directly connected to an SRX Series device. The traffic should flow unchanged as it passes through the SRX, and routing or switch lookups should not be performed.
However, the traffic should still be subjected to security policy checks.
What will provide this functionality?
- A. Mixed mode
- B. MACsec
- C. Secure wire
- D. Transparent mode
Answer: C
Explanation:
Secure wire mode on SRX devices allows traffic to flow transparently through the firewall without being routed or switched, while still applying security policies. This is ideal for scenarios wheretraffic inspection is required without altering the traffic path or performing additional routing decisions. For further details on Secure Wire, refer to Juniper Secure Wire Documentation.
In this scenario, you want traffic to pass through the SRX unchanged (without routing or switching lookups) but still be subject to security policy checks. The best solution for this requirement isSecure Wire.
* Explanation of Answer C (Secure Wire):
* Secure Wireallows traffic to flow through the SRX without any Layer 3 routing or Layer 2 switching decisions. It effectively bridges two interfaces at Layer 2 while still applying security policies. This ensures that traffic remains unchanged, while security policies (such as firewall rules) can still be enforced.
* This is an ideal solution when you need the SRX to act as a "bump in the wire" for security enforcement without changing the traffic or performing complex network lookups.
Juniper Security Reference:
* Secure Wire Functionality: Provides transparent Layer 2 forwarding with security policy enforcement, making it perfect for scenarios where traffic needs to pass through unchanged. Reference: Juniper Secure Wire Documentation.
NEW QUESTION # 46
Exhibit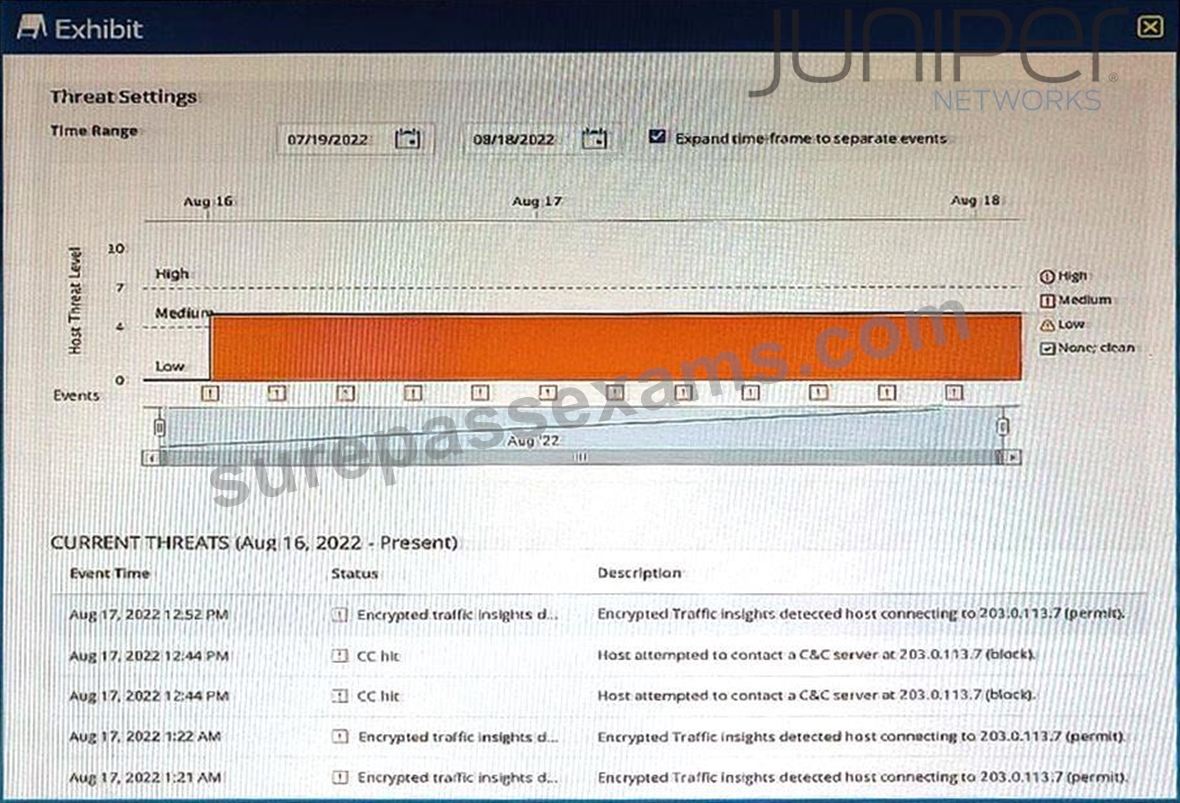
You are using ATP Cloud and notice that there is a host with a high number of ETI and C&C hits sourced from the same investigation and notice that some of the events have not been automatically mitigated.
Referring to the exhibit, what is a reason for this behavior?
- A. The ETI events are false positives.
- B. The infected host score is globally set bellow a threat level of 5.
- C. The C&C events are false positives.
- D. The infected host score is globally set above a threat level of 5.
Answer: A
NEW QUESTION # 47
Exhibit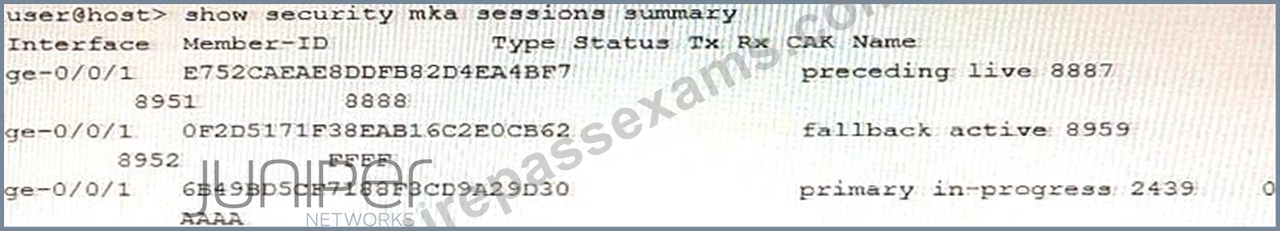
Referring to the exhibit, which two statements are true about the CAK status for the CAK named
"FFFP"? (Choose two.)
- A. SAK is successfully generated using this key.
- B. SAK is not generated using this key.
- C. CAK is not used for encryption and decryption of the MACsec session.
- D. CAK is used for encryption and decryption of the MACsec session.
Answer: B,D
NEW QUESTION # 48
You are deploying a virtualization solution with the security devices in your network Each SRX Series device must support at least 100 virtualized instances and each virtualized instance must have its own discrete administrative domain.
In this scenario, which solution would you choose?
- A. logical systems
- B. tenant systems
- C. VRF instances
- D. virtual router instances
Answer: A
NEW QUESTION # 49
You are requested to enroll an SRX Series device with Juniper ATP Cloud.
Which statement is correct in this scenario?
- A. Juniper ATP Cloud uses a Junos OS op script to help you configure your SRX Series device to connect to the Juniper ATP Cloud service.
- B. When the license expires, the SRX Series device is disenrolled from Juniper ATP Cloud without a grace period
- C. The only way to enroll an SRX Series device is to interact with the Juniper ATP Cloud Web portal.
- D. If a device is already enrolled in a realm and you enroll it in a new realm, the device data or configuration information is propagated to the new realm.
Answer: A
NEW QUESTION # 50
Referring to the exhibit, you are attempting to set up a remote access VPN on your SRX series devices.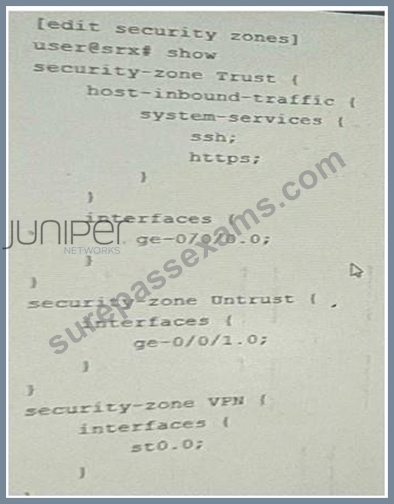
However you are unsure of which system services you should allow and in which zones they should be allowed to correctly finish the remote access VPN configuration Which two statements are correct? (Choose two.)
- A. You should add the host-inbound-traffic system-service ike statement to the VPN zone.
- B. You should add the host-inbound-traffic system-service ike statement to the Untrust zone.
- C. You should add the host-inbound-traffic system-service tcp-encap statement to the VPN zone
- D. You should add the host-inbound-traffic system-service tcp-encap statement to the Untrust zone
Answer: B,D
NEW QUESTION # 51
Exhibit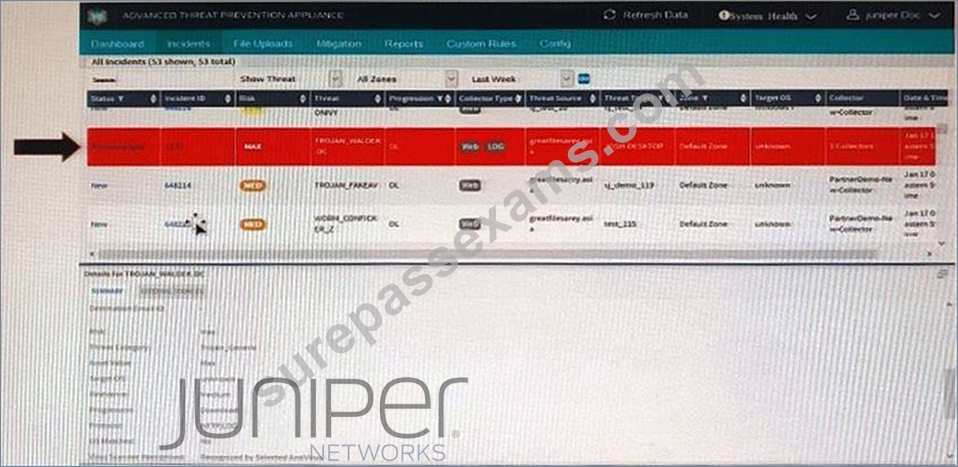
The highlighted incident (arrow) shown in the exhibit shows a progression level of "Download" in the kill chain.
What are two appropriate mitigation actions for the selected incident? (Choose two.)
- A. Immediate response required: Deploy IVP integration (if configured) to confirm if the endpoint has executed the malware and is infected.
- B. Immediate response required: Wipe infected endpoint hosts.
- C. Immediate response required: Block malware IP addresses (download server or CnC server)
- D. Not an urgent action: Use IVP to confirm if machine is infected.
Answer: A,C
NEW QUESTION # 52
You have deployed an SRX Series device at your network edge to secure Internet-bound sessions for your local hosts using source NAT. You want to ensure that your users are able to interact with applications on the Internet that require more than one TCP session for the same application session.
Which two features would satisfy this requirement? (Choose two.)
- A. address persistence
- B. double NAT
- C. persistent NAT
- D. STUN
Answer: A,C
Explanation:
Address persistence ensures that the same NAT IP address is used for all sessions originating from a single source IP. Persistent NAT maintains connections for applications needing multiple sessions, like VoIP.
Additional details are available in Juniper NAT Documentation.
For applications that require multiple TCP sessions for the same application session (such as VoIP or certain online games), the SRX device needs to handle NAT properly to maintain session continuity. Here's what helps:
* Address Persistence (Answer A): Address persistence ensures that multiple sessions initiated by the same internal host are mapped to the same external IP address. This is crucial for applications that use multiple TCP sessions to maintain a stateful connection with the external server.
Command Example:
bash
set security nat source persistent-nat address-persistence
* Persistent NAT (Answer C): This feature allows the external server to initiate new connections to the internal client using the same NAT translation. It's essential for applications that require consistent NAT mappings across multiple sessions.
Command Example:
bash
set security nat source persistent-nat permit target-host-port
These features ensure that applications with multiple TCP sessions work seamlessly across NAT.
NEW QUESTION # 53
......
Juniper JN0-637 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
Pass Your JN0-637 Exam Easily With 100% Exam Passing Guarantee: https://www.surepassexams.com/JN0-637-exam-bootcamp.html
JN0-637 Dumps are Available for Instant Access: https://drive.google.com/open?id=16m0RGumNvYBFxTNriDmLIR3WI6tM72dW