

Authentic Fortinet NSE7_EFW-7.0 Exam Dumps PDF - 2024 Updated
Get Prepared for Your NSE7_EFW-7.0 Exam With Actual 165 Questions
Fortinet NSE7_EFW-7.0 Exam is a certification exam designed for individuals who want to validate their skills and knowledge in deploying, configuring, and managing Fortinet's Enterprise Firewall solution. Fortinet NSE 7 - Enterprise Firewall 7.0 certification is suitable for network professionals who have experience in firewall administration and want to demonstrate their expertise in implementing and managing network security policies using Fortinet's products. NSE7_EFW-7.0 exam covers topics such as firewall policies, VPNs, SSL inspection, high availability, advanced authentication, and more.
NEW QUESTION # 88
View the exhibit, which contains the partial output of an IKE real-time debug, and then answer the question below.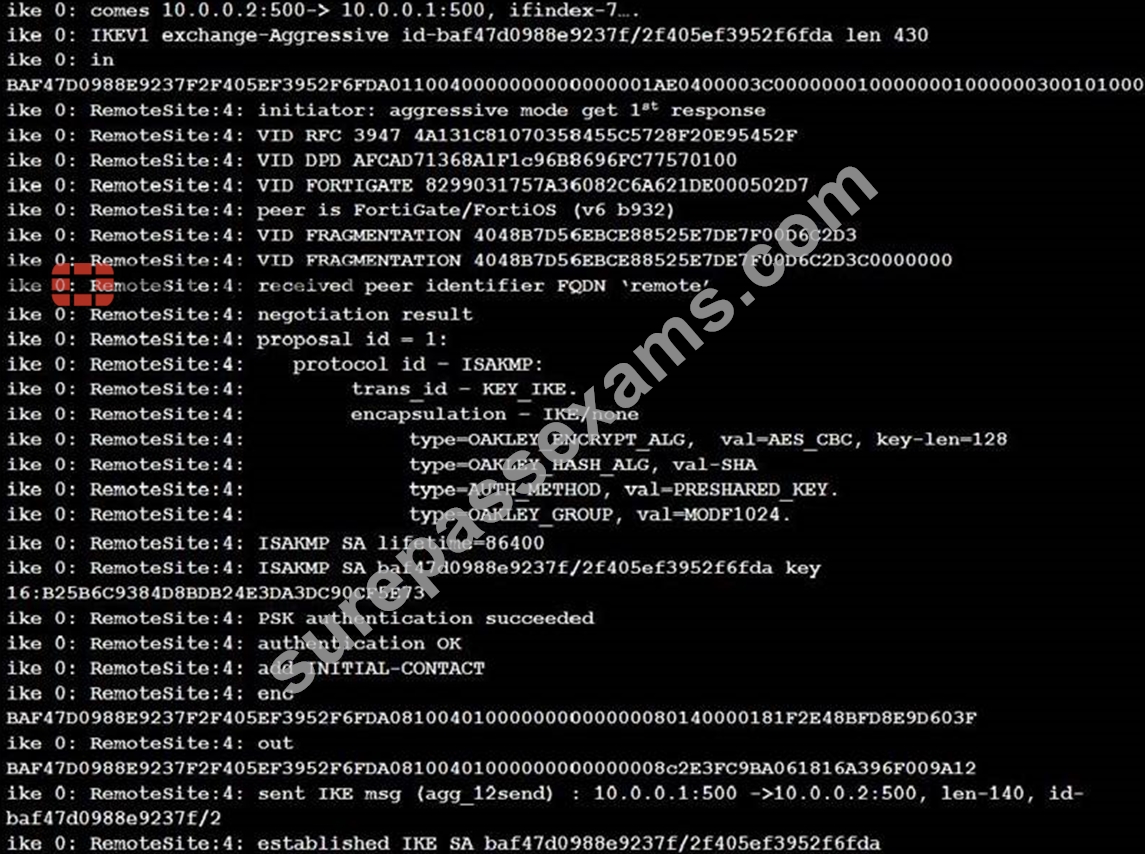
Which statements about this debug output are correct? (Choose two.)
- A. The remote gateway IP address is 10.0.0.1.
- B. It shows a phase 1 negotiation.
- C. The initiator has provided remote as its IPsec peer ID.
- D. The negotiation is using AES128 encryption with CBC hash.
Answer: B,C
NEW QUESTION # 89
The CLI command set intelligent-mode <enable | disable> controls the IPS engine's adaptive scanning behavior. Which of the following statements describes IPS adaptive scanning?
- A. Determines the optimal number of IPS engines required based on system load.
- B. Determines when it is secure enough to stop scanning session traffic.
- C. Choose a matching algorithm based on available memory and the type of inspection being performed.
- D. Downloads signatures on demand from FDS based on scanning requirements.
Answer: B
Explanation:
Configuring IPS intelligence Starting with FortiOS 5.2, intelligent-mode is a new adaptive detection method. This command is enabled the default and it means that the IPS engine will perform adaptive scanning so that, for some traffic, the FortiGate can quickly finish scanning and offload the traffic to NPU or kernel. It is a balanced method which could cover all known exploits. When disabled, the IPS engine scans every single byte.
config ips global set intelligent-mode {enable|disable} end
NEW QUESTION # 90
A FortiGate device has the following LDAP configuration: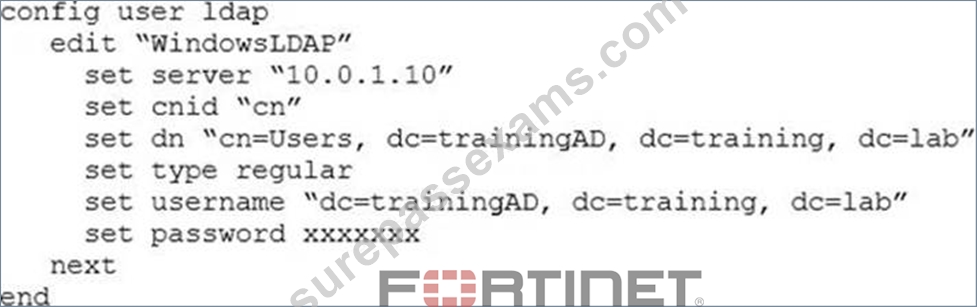
The administrator executed the 'dsquery' command in the Windows LDAp server 10.0.1.10, and got the following output:
>dsquery user -samid administrator
"CN=Administrator, CN=Users, DC=trainingAD, DC=training, DC=lab"
Based on the output, what FortiGate LDAP setting is configured incorrectly?
- A. password.
- B. username.
- C. cnid.
- D. dn.
Answer: B
NEW QUESTION # 91
Which of the following statements is true regarding a FortiGate configured as an explicit web proxy?
- A. FortiGate limits the number of workstations that authenticate using the same web proxy user credentials. This limit CANNOT be modified by the administrator.
- B. FortiGate limits the number of simultaneous sessions per explicit web proxy user. This limit CANNOT be modified by the administrator.
- C. FortiGate limits the number of simultaneous sessions per explicit web proxy user The limit CAN be modified by the administrator
- D. FortiGate limits the total number of simultaneous explicit web proxy users.
Answer: D
NEW QUESTION # 92
Which two configuration commands change the default behavior for content-inspected traffic while FortiGate is in conserve mode? (Choose two.)
- A. set av-failopen off
- B. set av-failopen pass
- C. set fail-open enable
- D. set ips fail-open disable
Answer: A,C
Explanation:
https://docs.fortinet.com/document/fortigate/7.2.4/administration-guide/194558/conserve-mode
NEW QUESTION # 93
Refer to the exhibit, which contains the partial output of a diagnose command.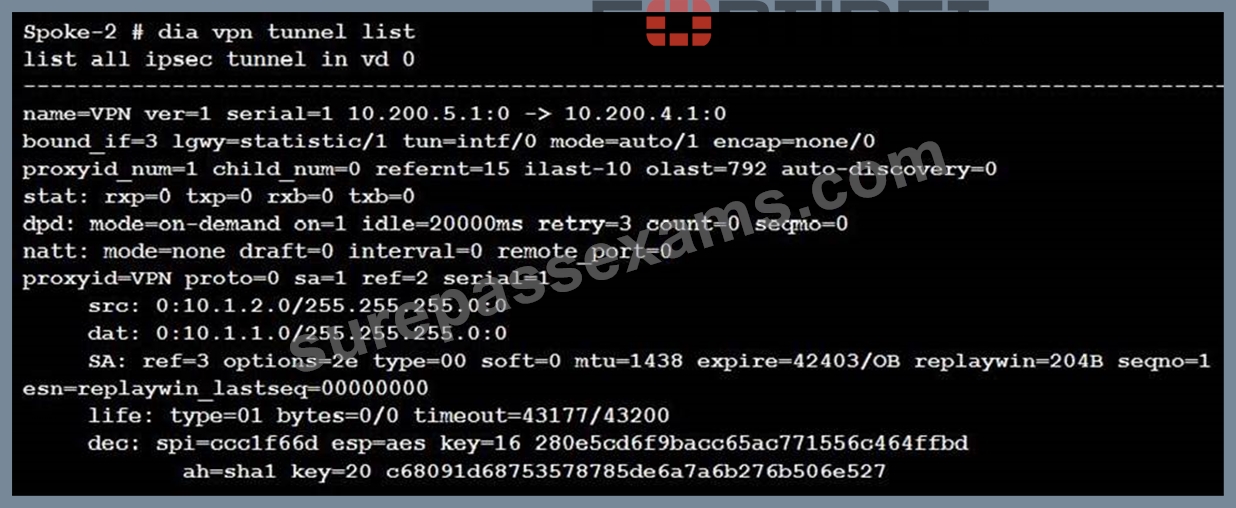
Based on the output, which two statements are correct? (Choose two.)
- A. The remote gateway IP is 10.200.4.1.
- B. Anti-replay is enabled
- C. Quick mode selectors are disabled.
- D. DPD is disabled.
Answer: A,B
NEW QUESTION # 94
View the central management configuration shown in the exhibit, and then answer the question below.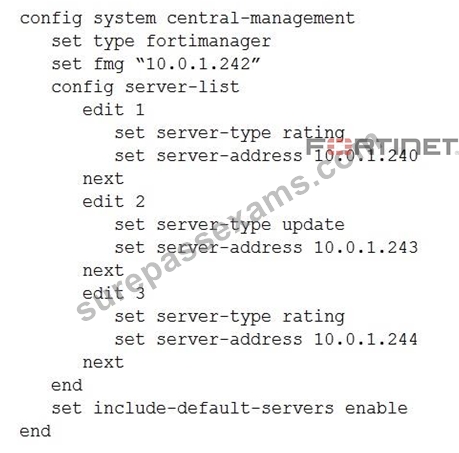
Which server will FortiGate choose for antivirus and IPS updates if 10.0.1.243 is experiencing an outage?
- A. 10.0.1.240
- B. 10.0.1.244
- C. One of the public FortiGuard distribution servers
- D. 10.0.1.242
Answer: C
NEW QUESTION # 95
A corporate network allows Internet Access to FSSO users only. The FSSO user student does not have Internet access after successfully logged into the Windows AD network. The output of the 'diagnose debug authd fsso list' command does not show student as an active FSSO user. Other FSSO users can access the Internet without problems. What should the administrator check? (Choose two.)
- A. The user student must belong to one or more of the monitored user groups.
- B. The user student must not be listed in the CA's ignore user list.
- C. At least one of the student's user groups must be allowed by a FortiGate firewall policy.
- D. The student workstation's IP subnet must be listed in the CA's trusted list.
Answer: B,C
Explanation:
https://kb.fortinet.com/kb/documentLink.do?externalID=FD38828
NEW QUESTION # 96
Refer to the exhibit, which contains partial output from an IKE real-time debug.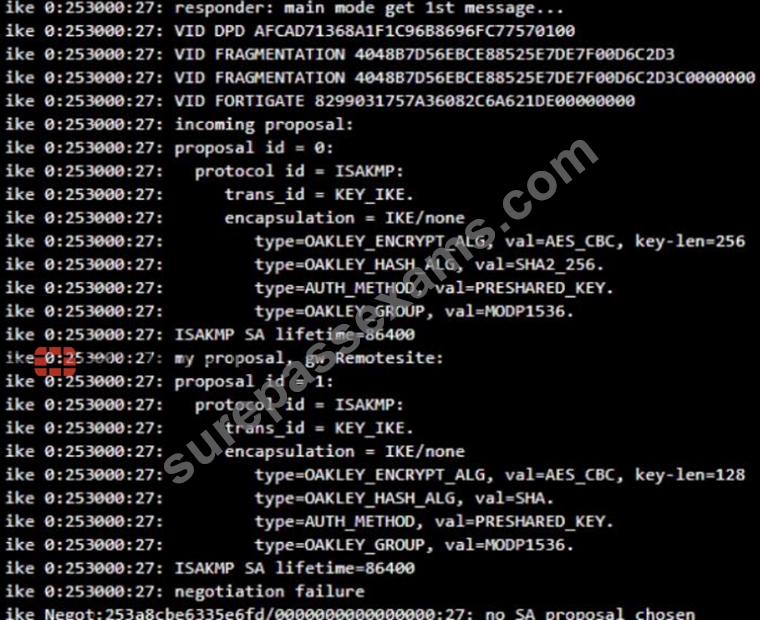
Why did the tunnel not come up?
- A. The local gateway has configured less secure encryption and hashing algorithms compared to the remote gateway.
- B. The Diffie-Hellman group does not match on the local and remote gateways.
- C. The proposal ID does not match between local and remote gateways.
- D. The encapsulation method for phase 2 is set to none on local and remote gateways.
Answer: A
Explanation:
local gateway: encryption AES-128, hash SHA remote gateway: encryption AES-256, hash SHA-256 So local gateway has less secure settings
NEW QUESTION # 97
View the exhibit, which contains the output of a debug command, and then answer the question below.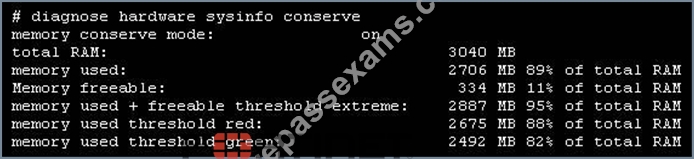
Which one of the following statements about this FortiGate is correct?
- A. It is currently in extreme conserve mode because of high memory usage.
- B. It is currently in proxy conserve mode because of high memory usage.
- C. It is currently in memory conserve mode because of high memory usage.
- D. It is currently in system conserve mode because of high CPU usage.
Answer: C
NEW QUESTION # 98
Refer to the exhibit, which shows the output of a debug command.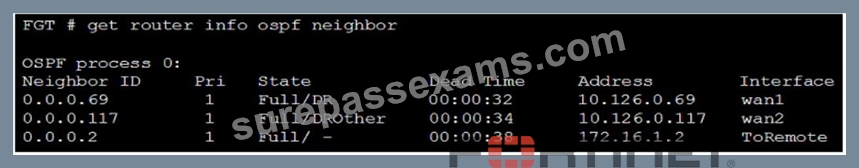
What can be concluded from the debug command output?
- A. There are more than two OSPF routers on the wan2 network.
- B. The local FortiGate has a different MTU value from the OSPF router with ID 0.0.0.2, based on the state information.
- C. The interface ToRemote is a broadcast OSPF network.
- D. The OSPF router with the ID 0.0.0.69 has its OSPF priority set to 0.
Answer: A
Explanation:
Enterprise_Firewall_7.0_Study_Guide-Online.pdf p 296
NEW QUESTION # 99
View the exhibit, which contains the output of a diagnose command, and then answer the question below.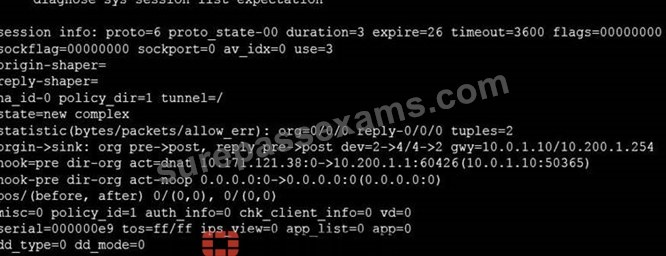
What statements are correct regarding the output? (Choose two.)
- A. This is an expected session created by an application control profile.
- B. Traffic in the original direction (coming from the IP address 10.171.122.38) will be routed to the next-hop IP address 10.0.1.10.
- C. Traffic in the original direction (coming from the IP address 10.171.122.38) will be routed to the next-hop IP address 10.200.1.1.
- D. This is an expected session created by a session helper.
Answer: C,D
NEW QUESTION # 100
Examine the following partial output from two system debug commands; then answer the question below.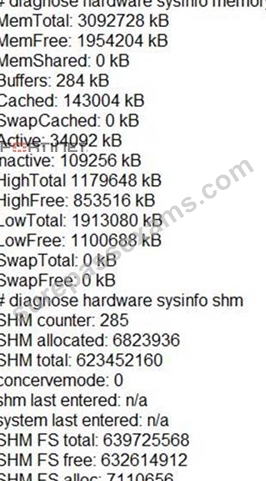
Which of the following statements are true regarding the above outputs? (Choose two.)
- A. Kernel indirectly accesses the low memory (LowTotal) through memory paging
- B. The Cached value is always the Active value plus the Inactive value
- C. The unit is in kernel conserve mode
- D. The unit is running a 32-bit FortiOS
Answer: B,D
NEW QUESTION # 101
Refer to the exhibits, which show the configuration on FortiGate and partial internet session information from a user on the internal network.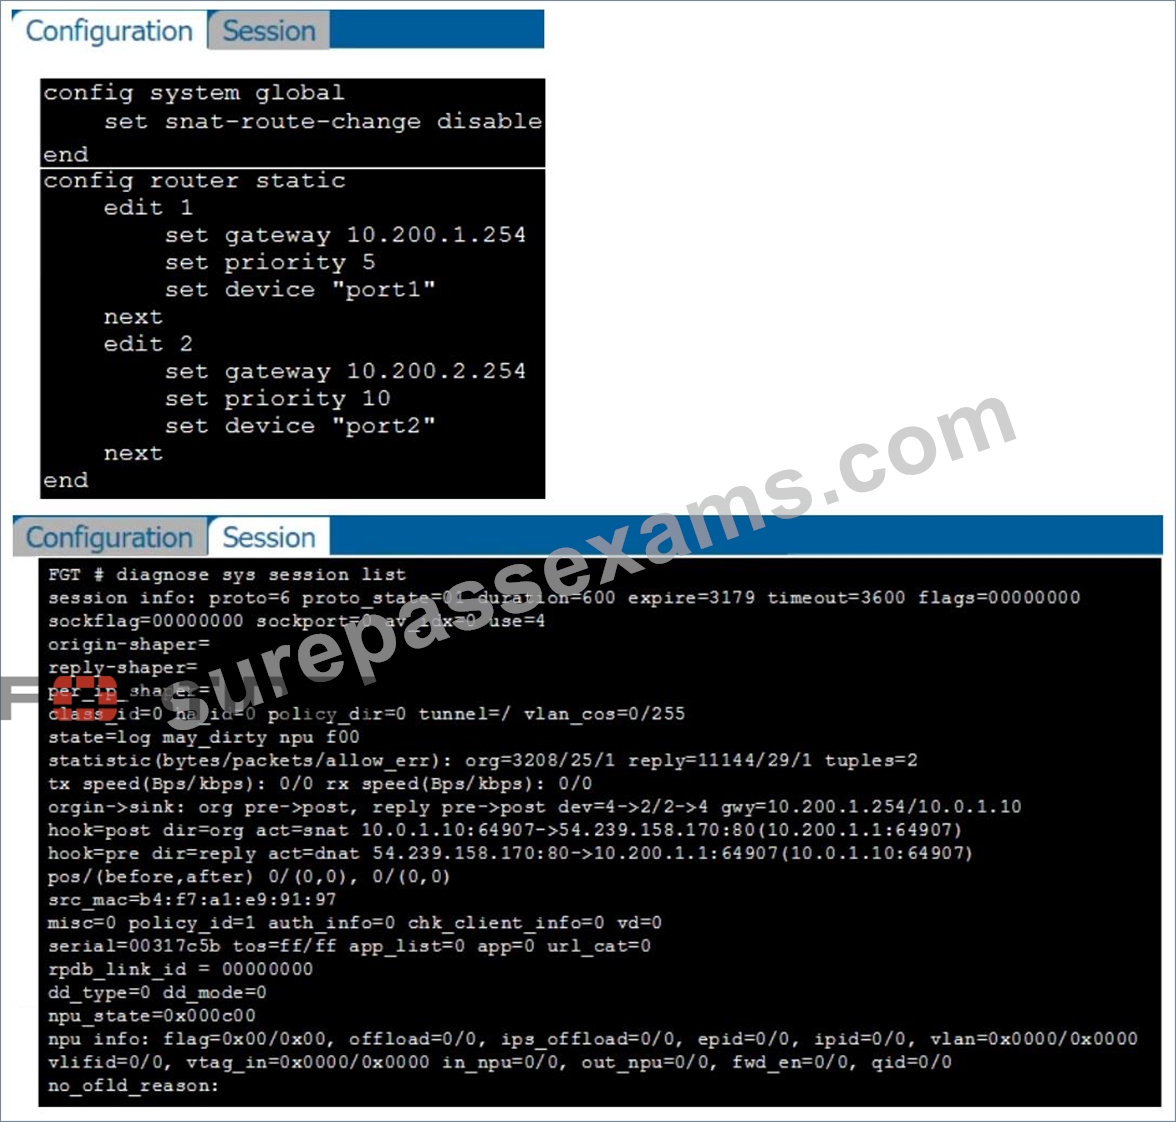
An administrator would like to test session failover between the two service provider connections.
What changes must the administrator make to force this existing session to immediately start using the other interface? (Choose two.)
- A. Change the priority of the port1 static route to 11.
- B. unset snat-route-change to return it to the default setting.
- C. Configure set snat-route-change enable.
- D. Change the priority of the port2 static route to 5.
Answer: A,C
Explanation:
Enterprise_Firewall_7.0_Study_Guide-Online.pdf p 148-149
NEW QUESTION # 102
Refer to the exhibit, which contains partial output from an IKE real-time debug.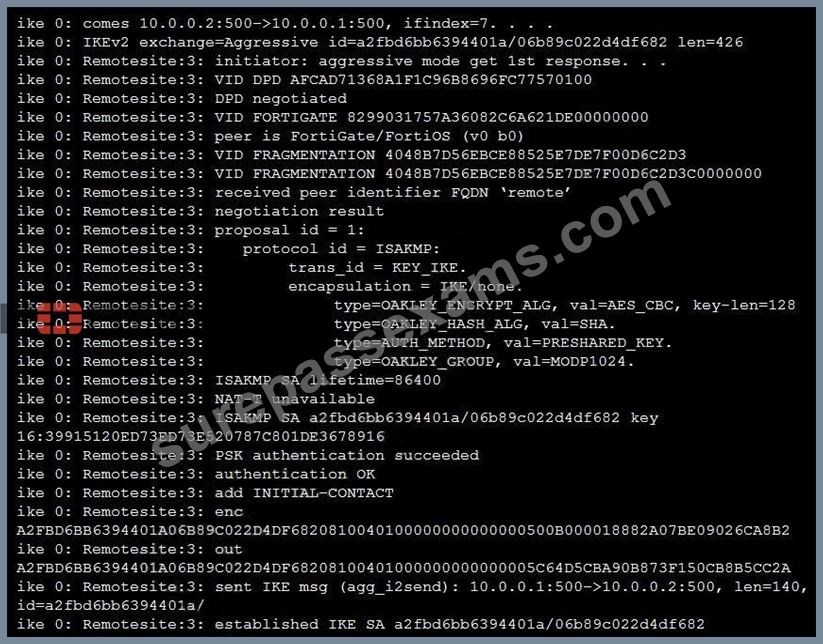
Which two statements about this debug output are correct? (Choose two.)
- A. The initiator provided remote as its IPsec peer ID.
- B. The remote gateway IP address is 10.0.0.1.
- C. It shows a phase 1 negotiation.
- D. The negotiation is using AES128 encryption with CBC hash.
Answer: A,C
NEW QUESTION # 103
View the exhibit, which contains the output of a diagnose command, and then answer the question below.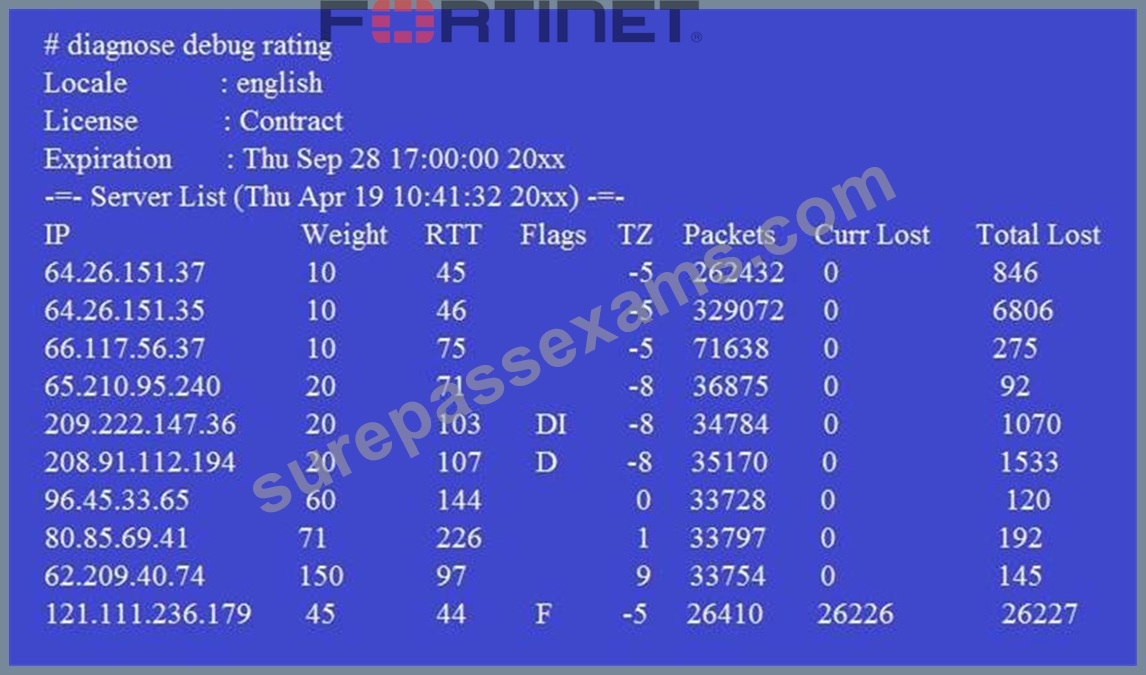
Which statements are true regarding the output in the exhibit? (Choose two.)
- A. Servers with the D flag are considered to be down.
- B. FortiGate will probe 121.111.236.179 every fifteen minutes for a response.
- C. Servers with a negative TZ value are experiencing a service outage.
- D. FortiGate used 209.222.147.3 as the initial server to validate its contract.
Answer: B,D
NEW QUESTION # 104
View the exhibit, which contains the output of a diagnose command, and then answer the question below.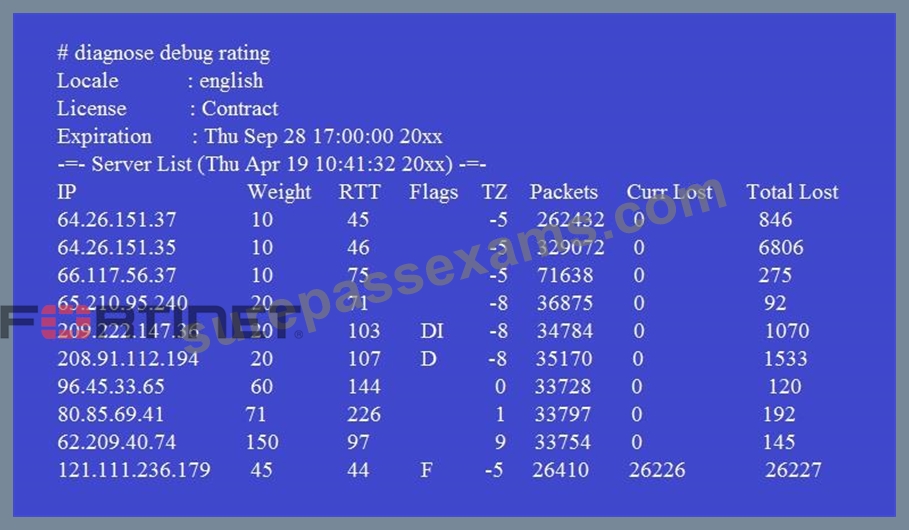
Which statements are true regarding the output in the exhibit? (Choose two.)
- A. Servers with the D flag are considered to be down.
- B. FortiGate will probe 121.111.236.179 every fifteen minutes for a response.
- C. Servers with a negative TZ value are experiencing a service outage.
- D. FortiGate used 209.222.147.3 as the initial server to validate its contract.
Answer: B,D
Explanation:
A - because flag is Failed so fortigate will check if server is available every 15 min D-state is I , contact to validate contract info
NEW QUESTION # 105
Refer to the exhibit, which shows a session entry. Which statement about this session is true?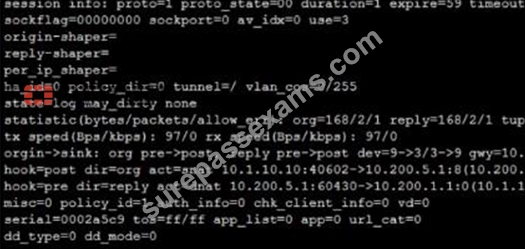
- A. It is a TCP session in close_wait state, from 10. l. 10.10 to 10.200.1.1.
- B. It is an ICMP session from 10.1.10.10 to 10.200.1.1.
- C. It is an ICMP session from 10.1.10.10 to 10.200.5. 1.
- D. It is a TCP session in the established state, from 10.1.10.10 to 10.200.5.1.
Answer: C
Explanation:
https://community.fortinet.com/t5/FortiGate/Troubleshooting-Tip-FortiGate-session-table-information/ta-p/196988?externalId=FD30042
NEW QUESTION # 106
Examine the output from the BGP real time debug shown in the exhibit, then the answer the question below: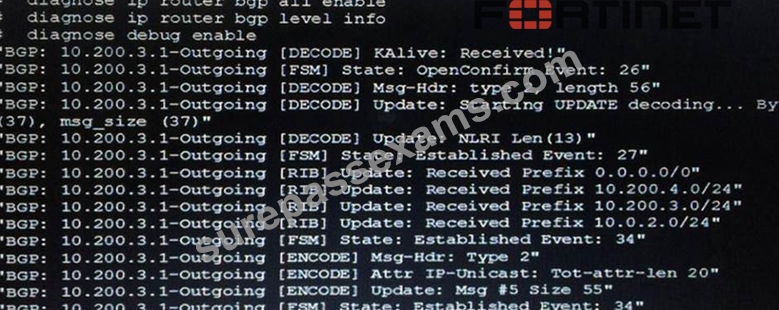
Which statements are true regarding the output in the exhibit? (Choose two.)
- A. The state of the remote BGP peer will go to Connect after it confirms the received prefixes.
- B. The state of the remote BGP peer is OpenConfirm.
- C. Local BGP peer received a prefix fora default route.
- D. BGP peers have successfully interchanged Open and Keepalive messages.
Answer: C,D
NEW QUESTION # 107
Which statement is true regarding File description (FD) conserve mode?
- A. FD conserve mode affects all daemons running on the device.
- B. Restarting the WAD process is required to leave FD conserve mode.
- C. A FortiGate enters FD conserve mode when the amount of available description is less than 5%.
- D. IPS inspection is affected when FortiGate enters FD conserve mode.
Answer: C
NEW QUESTION # 108
View the exhibit, which contains the output of a BGP debug command, and then answer the question below.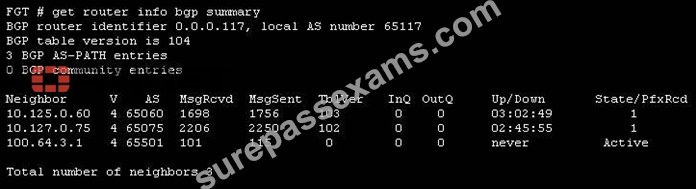
Which of the following statements about the exhibit are true? (Choose two.)
- A. Since the counters were last reset; the 10.200.3.1 peer has never been down.
- B. The local router has received a total of three BGP prefixes from all peers.
- C. The local router's BGP state is Established with the 10.125.0.60 peer.
- D. The local router has not established a TCP session with 100.64.3.1.
Answer: C,D
NEW QUESTION # 109
View the central management configuration shown in the exhibit, and then answer the question below.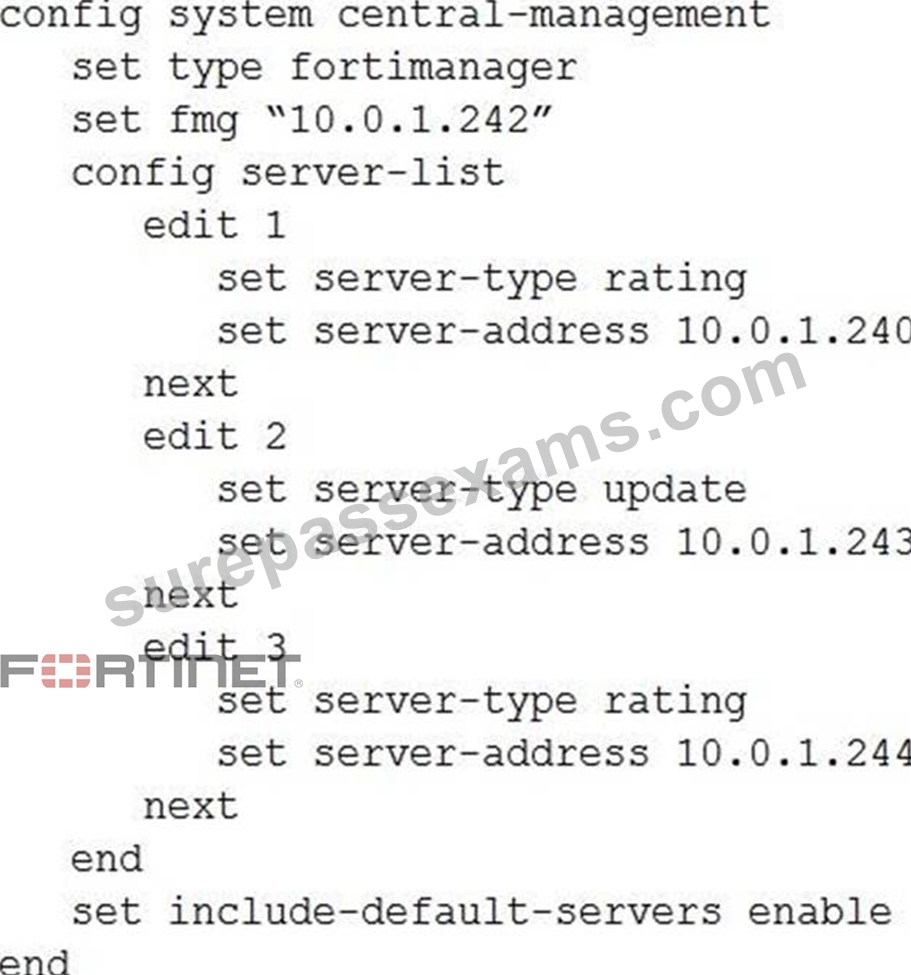
Which server will FortiGate choose for antivirus and IPS updates if 10.0.1.243 is experiencing an outage?
- A. 10.0.1.240
- B. 10.0.1.244
- C. One of the public FortiGuard distribution servers
- D. 10.0.1.242
Answer: C
NEW QUESTION # 110
A FortiGate device has the following LDAP configuration: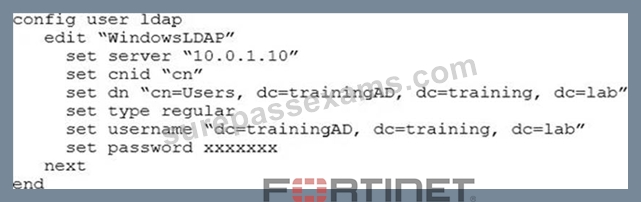
The administrator executed the 'dsquery' command in the Windows LDAp server 10.0.1.10, and got the following output:
>dsquery user -samid administrator
"CN=Administrator, CN=Users, DC=trainingAD, DC=training, DC=lab"
Based on the output, what FortiGate LDAP setting is configured incorrectly?
- A. password.
- B. username.
- C. cnid.
- D. dn.
Answer: B
NEW QUESTION # 111
......
Fortinet NSE7_EFW-7.0 Exam, also known as the Fortinet NSE 7 - Enterprise Firewall 7.0 Exam, is a certification exam that tests the skills and knowledge of IT professionals in designing, implementing, and managing enterprise-level firewall solutions using Fortinet technology. NSE7_EFW-7.0 exam is ideal for network administrators, security professionals, and other IT experts who work with Fortinet firewalls in a corporate environment.
Accurate & Verified New NSE7_EFW-7.0 Answers As Experienced in the Actual Test!: https://www.surepassexams.com/NSE7_EFW-7.0-exam-bootcamp.html
Valid NSE7_EFW-7.0 Test Answers Full-length Practice Certification Exams: https://drive.google.com/open?id=1nK2jUGFq11aVakJcysTKJiK0FBJQw1Kv